
NOW LAUNCHED
Security
Intelligence
Simple | Seamless | Secure
NIST 800-53
FedRAMP
OSCAL Native
02 /Connected security intelligence
See the risk.
Know what
depends on it.
A finding is only the starting point.
GovSecurity360 connects systems, controls, evidence, and owners—so your team can see what a risk affects and who needs to act.
Explore the connected workflow- 01Mission
- 02System
- 03Control
- 04Evidence
- 05Owner
GovSecurity360 / Platform briefFederal cybersecurity & compliance
GS360 / Connected contextIllustrative workflow · Not live system data
Evidence / Context
See the basis for the decision.
An overdue review is a finding to investigate—not proof of a compromise. Keep the observation and its supporting evidence together.
- Observed gap
- Access review is overdue
- Required follow-up
- Validate the review record
Trace the finding. Understand the consequence.Try the live demo
The platform at workLess disconnected work.
Less disconnected work.
More informed decisions.
01Live Risk CommandSee risk in context.
See risk in context.
Connect controls, risks, and POA&Ms to the systems and missions they support. Follow the evidence behind a finding, then see what needs attention.
- Unified risk dashboards
- System-to-evidence traceability
- Mission-aligned prioritization
02Mission WorkflowsMove the work forward.
Move the work forward.
Bring your people, systems, assets, and business processes into the same workflow. Coordinate ATO, FedRAMP, and CDM activities with the mission as the starting point.
- Connected security workflows
- OSCAL-enabled information
- Security and privacy in context
03AI NativePut AI to work.
Put AI to work.
Start with a system description. Use AI assistance to draft control narratives, identify information types, and prioritize risk actions, with your team reviewing the output.
- Assisted control narratives
- Information categorization
- Human review and accountability
BUILT FOR FEDERAL CYBERSECURITY & COMPLIANCE
NIST 800-53RMFFedRAMPOSCALFISMA
02 / Try GS360Your system.
Your system.
Its information.
A clearer starting point.
INFORMATION CATEGORIZATION / FIPS 199
Describe what your system does. Explore suggested information types and confidentiality, integrity, and availability impact levels.
AI-assisted output. Your team reviews the result.
Use fictional or sanitized information only.
Describe your system
Tip: you can also drag & drop a file into this box (.txt, .docx, .pdf).
Start with a sample system
Tip: use fictional or sanitized examples only.
03 /The people behind GS360
Experience on both sides
of the decision.
Security operators.
Risk executives. Federal leaders.
Our team brings experience across cybersecurity, privacy, data, and risk governance—and the realities of working across complex departments and agencies.
20+Years of experience
on average
on average
6Core
disciplines
disciplines
3Continents
of delivery
of delivery
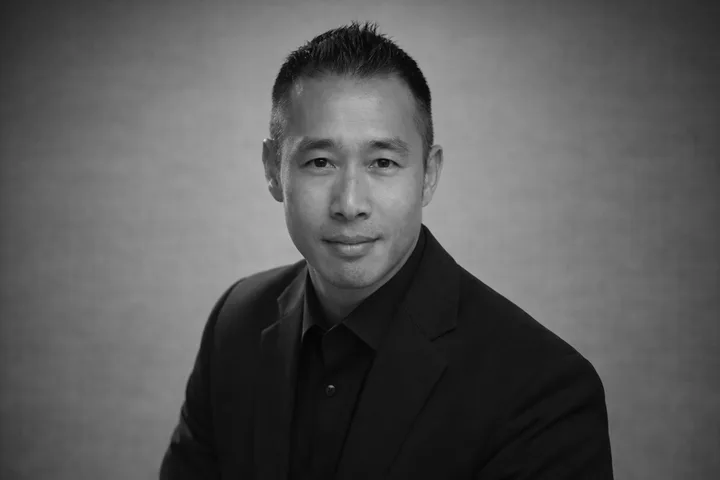
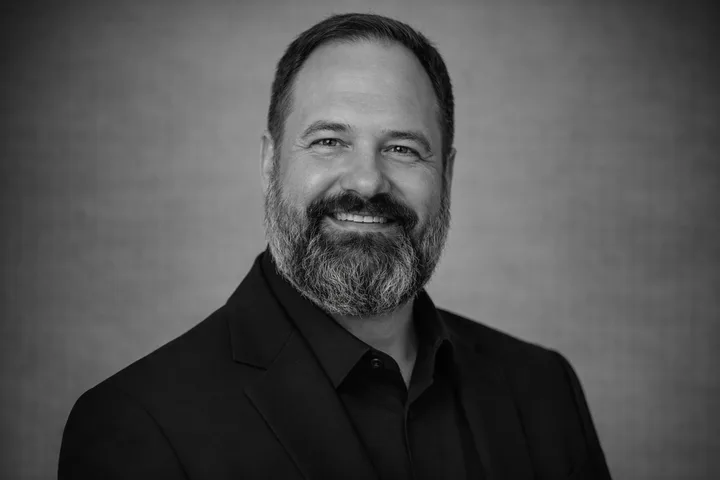
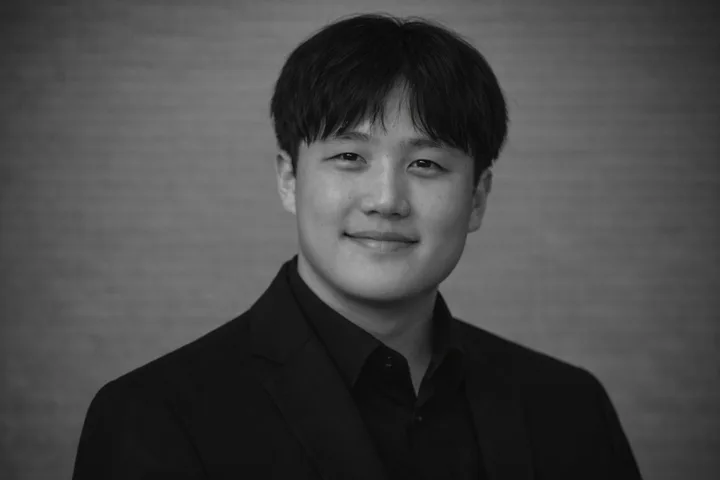
The founding team
GovSecurity360 / Leadership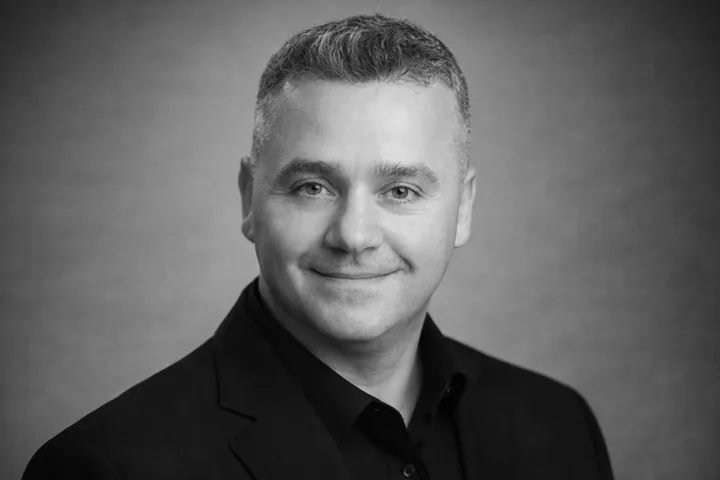
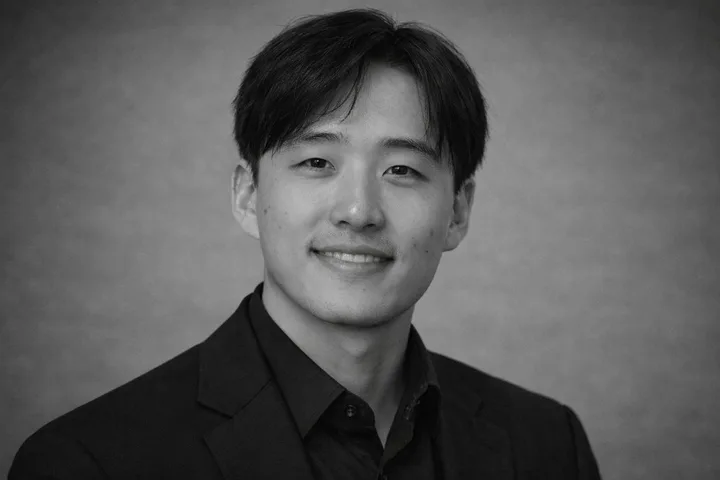
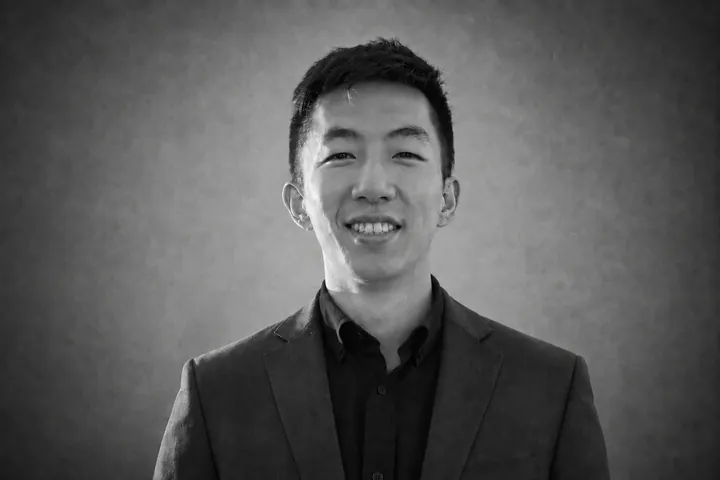
Josh Lee
Head of Operations
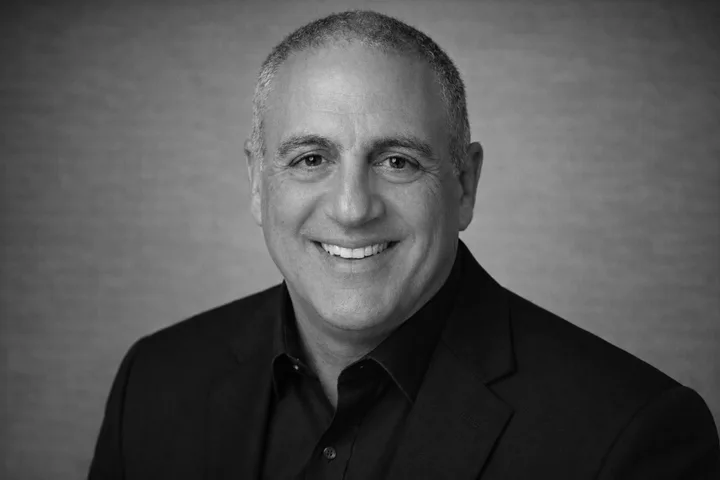
Eli Radi
Partner
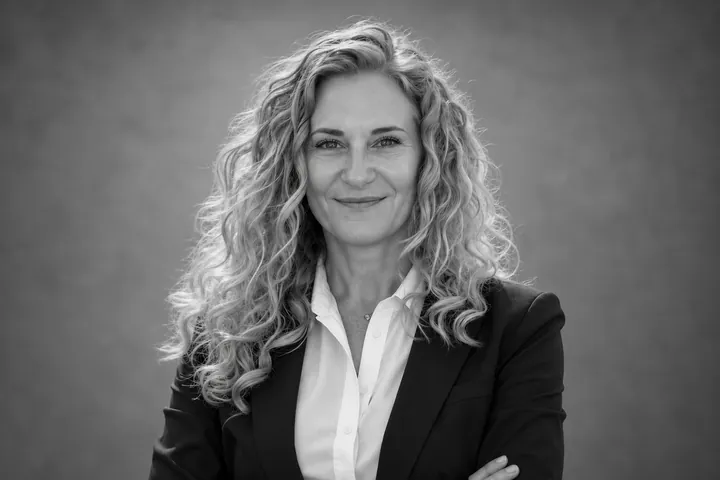
Karen Newnam
Executive Advisor, Marketing, Channels & Growth
Our starting point
Compliance should support the mission.
So should your software.
A conversation about your workflowWhere does your
Where does your
team need clarity?
Walk through your authorization workflow with our team. Tell us where systems, evidence, or responsibilities become disconnected, and we'll explore how GovSecurity360 could fit.
- Your systems and authorization priorities
- How your team manages controls and evidence
- What a connected workflow could look like